SPF, DKIM and DMARC in Plain English: Why Your Business Email Lands in Spam
Nathaniel Kober · · 8 min read
Gmail, Yahoo and Microsoft now expect every business domain to prove its email is real. Without three small settings called SPF, DKIM and DMARC, your invoices, quotes and contact-form messages can land in spam, or bounce. Here's what each one does, in plain English, and how to set them up safely.
Article
A customer swears they never got your quote. Your website's contact form "works," but nothing reaches your inbox. Your newsletter's open rate drops by half overnight. Often the cause isn't your message at all. It's that your domain can't prove the email really came from you.
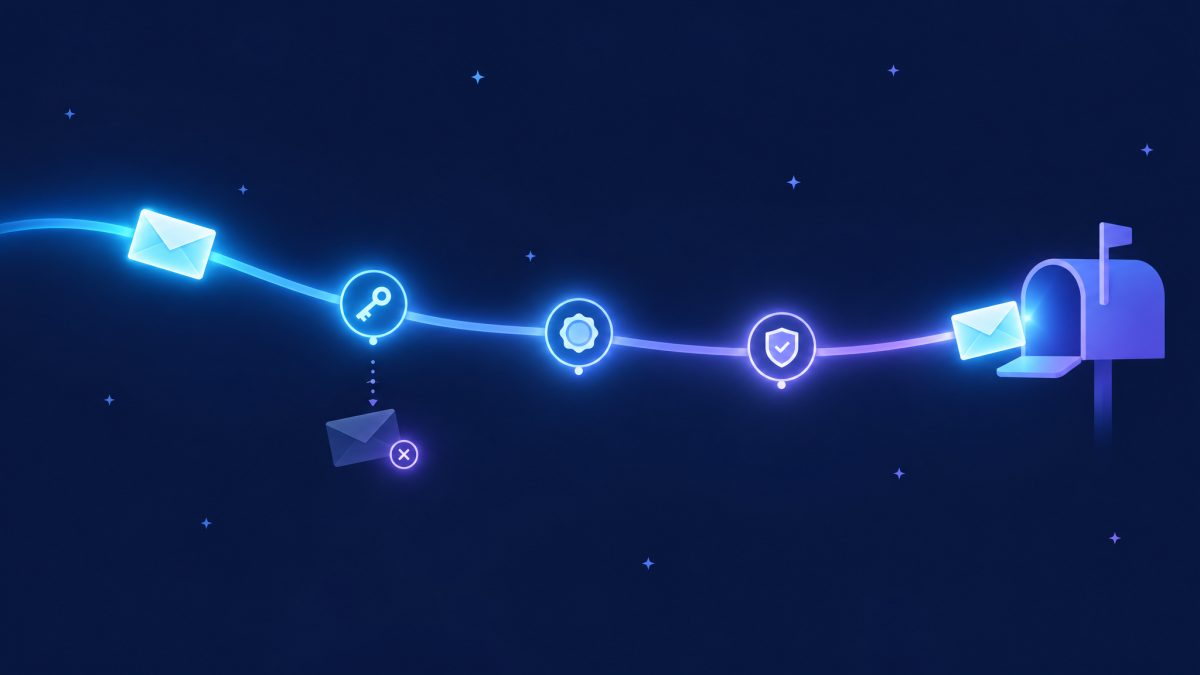
The short answer: SPF, DKIM and DMARC are three short text records added to your domain's settings. Together they tell email providers which services are allowed to send mail as your business, prove that messages weren't altered along the way, and say what to do with mail that fails those checks. Google, Yahoo and Microsoft now require them from anyone sending in bulk, and Google requires at least SPF or DKIM from every sender. Setting them up is usually an hour or two of careful work, and it also makes it much harder for scammers to send email pretending to be you.
SPF: the guest list
A list, published on your domain, of the services allowed to send email as you: your email provider, your newsletter tool, your website, your invoicing software. Mail from anywhere else looks suspicious.
DKIM: the wax seal
A digital signature added to each message. The receiving server checks it against a key published on your domain. If the seal is intact, the message really came from an approved sender and wasn't changed in transit.
DMARC: the instructions
Tells receiving servers what to do when a message claiming to be from you fails the checks: deliver it anyway, send it to spam, or reject it. It also sends you reports on who is sending mail in your name.
Why this suddenly matters
For years, these records were optional extras that large companies set up and small businesses ignored. That changed when the big mailbox providers started enforcing them.
- Google requires every sender to Gmail to set up SPF or DKIM. Senders of more than 5,000 messages a day must have SPF, DKIM and DMARC. Google began enforcing these rules in 2024 and has been tightening enforcement since, moving from temporary delays to outright rejections for mail that doesn't comply.
- Yahoo has the same split: SPF or DKIM for everyone, and SPF, DKIM, a passing DMARC record and one-click unsubscribe for bulk senders.
- Microsoft began enforcing similar rules for high-volume senders to Outlook.com, Hotmail and Live addresses on May 5, 2025. Mail that fails can be junked or rejected outright.
Your business probably doesn't send 5,000 emails a day. It doesn't matter as much as it sounds. Your newsletter platform pools your mail with other customers', the bulk thresholds count all of your domain's mail together, and providers increasingly treat unauthenticated mail from any sender with suspicion. The safe assumption in 2026 is that every business domain needs all three.
| Provider | All senders | Bulk senders (more than 5,000 messages a day) |
|---|---|---|
| Google (Gmail) | SPF or DKIM | SPF, DKIM and DMARC, plus one-click unsubscribe on marketing mail and a low spam complaint rate |
| Yahoo and AOL | SPF or DKIM; spam complaint rate below 0.3% | SPF and DKIM; a passing DMARC record at p=none or stricter, aligned with your From address; one-click unsubscribe honored within 2 days |
| Microsoft (Outlook.com, Hotmail, Live) | Authentication strongly recommended | SPF, DKIM and DMARC at p=none or stricter, aligned with SPF or DKIM; enforced since May 5, 2025 |
It also protects your customers
Authentication isn't only about getting your mail delivered. It's about stopping someone else from sending mail that looks like yours.
Business email compromise, where criminals impersonate a company or an executive to redirect payments, is one of the costliest crimes the FBI tracks. Its Internet Crime Complaint Center received 21,442 business email compromise complaints in 2024, with losses close to $2.8 billion, and nearly $8.5 billion over the three years from 2022 through 2024.
A DMARC record set to quarantine or reject tells Gmail, Outlook and others to stop mail that claims to come from your domain but doesn't. It won't stop every scam, since criminals can still register look-alike domains, but it closes the easiest door. For older customers, who are frequent targets of impersonation scams, that protection matters even more, as we cover in designing websites for older adults.
Adoption is still patchy. An EasyDMARC study of 1.8 million domains published in April 2026 found that about 48% had no valid DMARC record at all, and only about 23% had a policy strict enough to actually block spoofed mail.
The hidden senders: your website and your apps
Most small businesses send email from more places than they realize:
- Your regular email, such as Google Workspace or Microsoft 365
- Your website, which sends contact-form notifications, order confirmations and password resets
- Your newsletter tool, such as Mailchimp or Constant Contact
- Your invoicing, booking, CRM or point-of-sale software
Each one has to be included in SPF, and ideally set up to sign with DKIM on your domain. Skip one and its mail fails, often quietly.
Websites are a common culprit. Out of the box, WordPress sends mail directly from the web server, which usually isn't on your SPF list and can't sign with your DKIM key. The fix is to route website mail through an authenticated email service using an SMTP plugin, which is one of the settings a good WordPress care plan checks.
A safe setup plan
- List everything that sends email as your domain. Email provider, website, newsletter, invoicing, booking, CRM, point of sale. Ask whoever set each one up.
- Publish one SPF record. A domain can have only one. Combine every approved sender into it. SPF also has a limit of 10 DNS lookups, so a long list of services can quietly break it.
- Turn on DKIM for each service. Most providers give you a record or two to add to your domain, then a button to start signing.
- Fix your website's mail. Send it through an authenticated service rather than straight from the web server.
- Publish DMARC at p=none, with reporting turned on. Nothing gets blocked yet. You start receiving reports showing who is sending mail as you, and whether it passes.
- Read the reports and fix the gaps. A free or low-cost DMARC report reader turns the raw reports into something readable. Expect to find at least one sender you forgot.
- Tighten gradually. Move to quarantine, which sends failing mail to spam, and then to reject once everything legitimate passes.
- Keep it current. Every time you add a new tool that sends email, add it to SPF and DKIM before you start using it.
These records live in your domain's DNS settings, wherever your domain is managed. If you don't know who controls your domain, that's worth finding out before anything else. Losing access to it is far worse than any spam folder.
A few more habits that help
- Send business mail from your own domain, not a free Gmail or Yahoo address. You can't authenticate a domain you don't own.
- Make unsubscribing easy on marketing mail, and honor requests quickly. It's required for bulk senders, and the law already requires a working opt-out, as we explain in who regulates your website?
- Only email people who asked to hear from you. Spam complaints count against you no matter how well your records are set up.
As a Cloudflare agency partner, Kosmic Edge manages DNS for many of the sites we host, and we set up SPF, DKIM and DMARC as part of our website development and hosting work, including routing website mail through an authenticated service.
Frequently asked questions
What is SPF in email?
SPF (Sender Policy Framework) is a record on your domain that lists the services allowed to send email on your behalf. Receiving servers check it to decide whether a message claiming to be from you came from an approved source.
What is DKIM?
DKIM (DomainKeys Identified Mail) adds a digital signature to each message. Receiving servers check the signature against a key published on your domain to confirm the message came from an approved sender and wasn't altered.
What is DMARC?
DMARC tells receiving servers what to do with mail that claims to be from your domain but fails SPF and DKIM checks: deliver it, send it to spam or reject it. It also sends you reports about who is sending mail as your domain.
Do small businesses need DMARC?
Google requires at least SPF or DKIM from every sender, and Google, Yahoo and Microsoft require DMARC from bulk senders. Even below those thresholds, DMARC improves delivery and makes it harder for criminals to impersonate your business.
Why do my website's contact form emails go to spam?
WordPress and many other website platforms send mail straight from the web server by default, which usually fails SPF, DKIM and DMARC checks. Routing website mail through an authenticated email service usually fixes it.
Related reading
- What managed WordPress care actually covers, and why sites break without it.
- Who regulates your website? Including the rules for marketing email and texts.
- Designing websites for older adults: including how to help customers spot scams.
- How to show up in AI answers: a 2026 guide for local businesses.
Sources
- Google Workspace Admin Help, About authentication methods (updated October 2026)
- Yahoo Sender Hub, Sender best practices
- Red Sift, Gmail's enforcement ramps up: what bulk senders need to know
- Mailgun, Microsoft sender requirements
- Nacha, FBI's IC3 finds almost $8.5 billion lost to business email compromise in last three years (April 2025)
- EasyDMARC, 2026 DMARC Adoption & Enforcement Report (April 2026)
This article reflects mailbox provider requirements as of October 2026. Providers update their rules regularly, so check their sender guidelines before major changes.